 Install free
Introduction
Since the General Data Protection Regulation took effect in 2018 and the ePrivacy Directive set rules for storing information on a user’s device, cookie consent banners have been mandatory for any site using non-essential cookies for visitors in the European Union and the UK. This applies regardless of where your business is headquartered.
If your site runs analytics tools like Google Analytics, advertising pixels from Meta or TikTok, or any personalization or tracking cookies, you need a cookie banner for EU/UK visitors. These rules extend to similar tracking technologies such as local storage, fingerprinting, and SDKs.
By 2026, over 20 US states have enacted comprehensive data privacy regulations. While most follow an opt-out consent model rather than GDPR-style opt-in, they still require notice at or before data collection and simple mechanisms for users to refuse targeted advertising or sale of personal data.
For Shopify stores and other e-commerce sites, cookie banners have become a standard trust signal. Research shows that 44% of users trust brands more with transparent data use, and cookie banners can enhance user engagement and trust when done well.
 Pandectes GDPR ComplianceThe most popular & reviewed GDPR app for ShopifyInstall free on Shopify
What Counts as Personal Data and Cookies Under GDPR
Under GDPR, personal data is any information relating to an identified or identifiable person. This goes well beyond names and emails; it includes IP addresses, cookie IDs, device identifiers, and behavioral data collected through browsing patterns.
The types of cookies and technologies that typically involve processing personal data include:
- HTTP cookies (first-party and third-party cookies)
- Local storage and session storage
- Tracking pixels (Meta Pixel, TikTok Pixel, etc.)
- Fingerprinting technologies that create unique device profiles
- Mobile SDKs in apps that transmit identifiers
- Session replay tools where individual behavior can be singled out
Strictly necessary cookies, those required for cart functionality, checkout, login sessions, or security, are exempt from consent under GDPR. However, analytics, marketing, and most personalization cookies require prior consent before they fire.
Even “anonymous” analytics deployments like standard Google Analytics 4 can still involve personal data under European regulator interpretation, because users may be singled out indirectly through IP addresses combined with other signals. The safe approach: treat analytics cookies as requiring consent in EU/UK settings.
GDPR and ePrivacy: Core Cookie Banner Requirements
GDPR (Articles 6 and 7) and the ePrivacy Directive together require valid consent before storing or accessing non-essential cookies on a user’s device. GDPR requires explicit consent before setting non-essential cookies, and non-essential cookies must not load before user consent is obtained.
What qualifies as valid consent under these privacy laws:
- Freely given: Users cannot be forced or pressured. Designs that block access to content until consent is obtained, known as cookie walls, are considered deceptive and generally non-compliant.
- Specific: Consent must relate to clearly defined purposes (analytics, marketing, etc.), not a blanket “agree to everything.”
- Informed: GDPR compliance requires clear, plain language without legal jargon. Visitors must understand what they are consenting to.
- Unambiguous: Require an affirmative action. Pre-ticked boxes, implied consent from scrolling, or “by continuing to use this site you agree” banners do not count.
GDPR mandates opt-in consent for non-essential cookies. A GDPR compliant cookie banner must block cookies by default, and only fire tracking scripts, marketing tags, and analytics after the user has provided explicit consent. Under GDPR, fines can reach €20 million or 4% of global annual revenue, whichever is higher.
Designing a Compliant Cookie Banner: No Dark Patterns
Regulators now focus heavily on cookie banner layout and design. Banners that visually push “Accept” while hiding or minimizing “Reject” undermine valid consent and have triggered significant enforcement actions. Users prefer clear consent options to feel in control of their data.
Best practices for a user-friendly cookie banner:
- Place “Accept all” and “Reject all” (or “Reject non-essential cookies”) buttons on the same first layer, with equal prominence-same size, same color weight, same number of clicks
- Include a “Customize choices” or “Manage preferences” link for granular control
- Use plain, honest labels: “Accept all cookies,” “Reject non-essential cookies,” “Customize choices”
- Never use pre-ticked checkboxes for consent-this violates GDPR requirements
Dark patterns to avoid include: tiny or low-contrast reject links, misleading wording like “OK” or “Continue” instead of clear accept/reject labels, requiring multiple steps to refuse cookies while accept is a single click, and using deceptive color choices that steer users toward accepting.
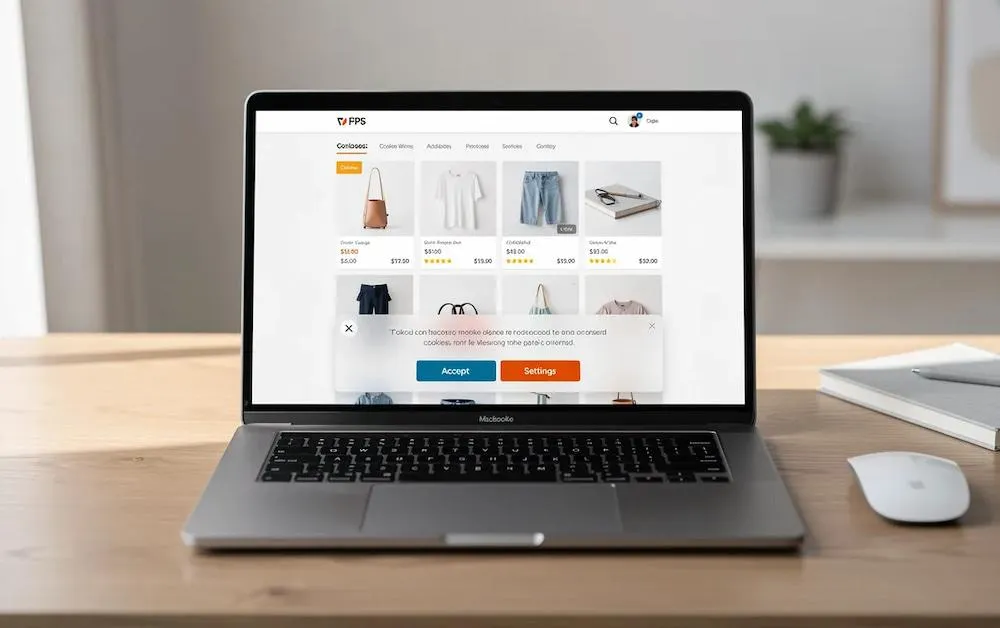
Cookie banners must provide equal options to accept or reject cookies. Users must also be able to withdraw consent easily at any time. This means a persistent link or icon, such as “Cookie Settings” in the footer, must allow visitors to reopen the consent banner and change their consent preferences whenever they choose.
A Google-Approved Consent Platform for Shopify
Pandectes is an official Google Certified Consent Management Platform and is fully compatible with Google Consent Mode v2 and global privacy regulations.
View the App on ShopifyKey Elements Your GDPR Cookie Banner Must Include
Think of this as your GDPR cookie banner checklist. Every compliant cookie banner should contain these core elements:
- Concise first-layer text that tells visitors the site uses cookies, states the purposes (basic functions, analytics, targeted advertising), and explains that users can accept, reject cookies, or customize
- A link to a detailed cookie policy or a separate page within your privacy notice where each cookie category, provider, purpose, and lifespan is documented; cookie banners must include clear links to privacy and cookie policies
- Granular controls by category: strictly necessary (always on), preferences, statistics/analytics, marketing/targeted advertising, with clear opt-in toggles for each non-essential category so users can opt-out of non-essential cookies by category
- Jurisdiction-aware localization: EU visitors see GDPR-style opt-in consent, US visitors may see opt-out language where applicable, and the banner on your website should adapt by language to inform visitors in their own language
- Accessibility: keyboard navigation, screen reader labels, sufficient color contrast, and focus management are part of cookie banner compliance, not just a UX preference.
Transparent cookie practices can improve brand reputation. The goal is to inform users clearly and give them real control over data collected from their visits.
Opt-In vs Opt-Out: Matching Consent to Each Law
Globally, there are two main consent models, and cookie consent banners vary depending on which law applies. Getting this wrong is one of the most common compliance failures.
Opt-in consent (GDPR, UK GDPR, Brazil’s LGPD): Non-essential cookies must be blocked until the visitor actively accepts via the consent banner. Opt-in consent requires user agreement before data collection. Continuing to browse is not valid consent. Opt-in consent is common in the EU and Brazil.
Opt-out consent (CCPA/CPRA, Colorado, Connecticut, and most US state laws): Opt-out consent assumes user consent unless revoked. Sites must provide clear notice and an easy way to opt-out of sale, sharing, or targeted advertising, including honoring Global Privacy Control (GPC) browser signals. Opt-out consent is prevalent in US privacy laws, and the CCPA mandates an opt-out option for data processing.
The Connecticut Data Privacy Act requires clear notice and opt-out options for sale, targeted advertising, and profiling, with opt-in consent required for processing sensitive personal data.
A critical distinction: a notice-only cookie banner saying “By using this site you consent…” is not valid consent under GDPR. While such language may appear in some US-only contexts, it fails the informed consent and explicit consent standards of European law.
Beyond Europe: US State & Other Global Cookie Banner Rules
The US privacy landscape has expanded rapidly. Here are the key regimes shaping cookie usage requirements:
California (CCPA/CPRA) requires a “Notice at Collection” and a clear “Do Not Sell or Share My Personal Information” link. California’s CPRA allows opt-out consent for data processing, with special opt-in protections for minors under 16. California fines can reach $7,500 per violation under CCPA. In 2022, Sephora was fined $1.2 million for CCPA violations-a warning to e-commerce businesses that CCPA enforcement is real.
Colorado Privacy Act (CPA) grants consumers the right to opt-out of targeted advertising and profiling, with explicit opt-in consent required for processing sensitive personal information. Cookie banners must surface these choices clearly.
Connecticut Data Privacy Act (CTDPA) follows the same opt-out model for sale and targeted advertising, with opt-in for sensitive data. Banners need to reflect both opt-in and opt-out signals depending on the data type.
By 2026, around 20 US states, including Virginia, Utah, Indiana, Kentucky, Rhode Island, Oregon, and others, have privacy laws influencing cookie banner design, especially around targeted advertising, personal data collection, and GPC signals.
In other major regimes (Canada’s PIPEDA, China’s PIPL, Japan’s APPI, Brazil’s LGPD, UK GDPR), cookie banners or similar consent notices are now standard tools for obtaining and documenting consent for collecting data and requesting consent from visitors.
Consent Management Platforms: Why a CMP Matters in 2026
A consent management platform is a tool that displays cookie banners, blocks tags until consent, logs choices, geotargets experiences by jurisdiction, and updates automatically as data privacy laws evolve. If you’re managing compliance manually, you’re almost certainly missing something.
Critical CMP features to look for:
- Automated cookie scanning and categorization of all cookies and similar tracking technologies on your site
- Script blocking that prevents non-essential cookies from firing until consent is granted
- Consent logs with timestamps, device/browser info, banner version, and event history
- Support for Google Consent Mode v2 to pass consent signals to Google services
A good CMP provides geolocation and rule-based behavior: showing GDPR-style opt-in banners to EU/UK visitors, CTDPA- and CCPA-compliant opt-out controls for US states, and different flows for Brazil, Canada, and beyond. It integrates with tools like Google Analytics, Google Ads, and Meta Pixel so that only consented data is sent, crucial for both cookie banner compliance and data accuracy.
Pandectes GDPR Compliance Shopify app, a Google-certified consent management platform built for Shopify, provides prebuilt jurisdiction-aware banner templates, auto-scanning of Shopify apps for new cookies, multilingual support, and Shopify-specific integrations. Effective cookie banners can lead to higher data sharing rates when visitors feel genuinely in control.
Implementing a GDPR-Ready Cookie Banner on a Shopify Store
For Shopify merchants, here is a practical implementation flow using a tool like Pandectes:
- Install and scan: Add the Pandectes GDPR Compliance app from the Shopify App Store. Run an automated scan to detect every cookie, tag, and third-party app active on your store, mapping them to categories.
- Configure your banner: Choose a cookie banner layout (bottom bar, center modal), select languages, configure jurisdictions (EU/EEA, UK, US states, Brazil), and map cookie categories to the correct legal bases-consent for GDPR regions, legitimate interest only where narrowly allowed.
- Block by default: The app should block non-essential cookies by default and fire scripts only after the user has provided opt-in consent (for GDPR regions) or has not opted out (for certain US contexts). This ensures no tracking cookies load before consent.
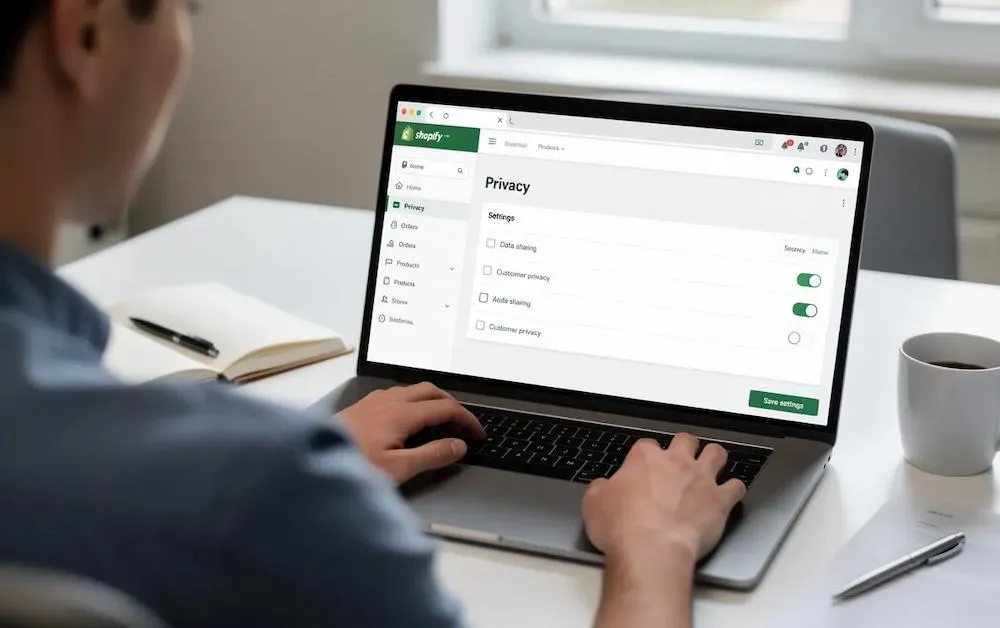
- Enable preference management: Pandectes logs consent in a secure, audit-ready manner and surfaces a “Privacy choices” or “Cookie settings” link in your storefront footer so visitors can change preferences, revoke consent, or opt-out at any point.
Make Your Shopify Store GDPR & Cookie Compliant in Minutes
Start Free on ShopifyConsent Logging, Audits, and Google Consent Mode v2
By 2026, regulators expect not just banners but robust consent records that can be produced on demand during investigations. Consent must be logged and retrievable for audits under GDPR.
What must be logged for each visitor interaction:
- Date, time, and region of the visitor
- Device and browser type
- Banner version shown at the time of interaction
- Specific cookie categories or vendors accepted or rejected
- Any subsequent changes or withdrawals of consent
Google Consent Mode v2 is now a baseline expectation. Your CMP must send consent signals-such as ad_storage, analytics_storage, ad_user_data, and ad_personalization-to Google so that Google Analytics and Ads respect user choices. Without the right signals, measurement breaks, or you risk non-compliance.
With Consent Mode v2, even when users opt-out, Google can use aggregated or modeled data in certain configurations, but only within the limits allowed by GDPR and similar laws, and only if consent flags are correctly set. Pandectes connects banner choices directly to Google Consent Mode v2 so Shopify merchants maintain measurement continuity while staying compliant.
Common Cookie Banner Mistakes That Break Compliance
Even well-intentioned sites get these wrong. Each of these errors can trigger enforcement:
- Tracking scripts firing before consent: Loading Google Analytics or advertising pixels on page load before the visitor responds to the banner. In 2022, CNIL fined Microsoft €60 million for cookie consent violations. The CNIL fined Google €150 million for consent violations in 2025, and Shein was fined €150 million for placing ad cookies before consent.
- Reject harder than accept: Offering a prominent “Accept” button while burying “Reject” in a secondary layer or behind multiple clicks. Cookie banners must let users reject cookies easily from the first screen.
- Pre-ticked toggles: Having analytics or marketing toggles pre-selected violates the requirement for obtaining explicit consent through an affirmative action.
- Failing to honor GPC signals: Even if a surface-level banner exists, ignoring opt-out rights under CPRA, CPA, or CTDPA creates liability.
- Never updating the banner: Many store owners add a free cookie banner once but never update it when they install new Shopify apps that set additional cookies, creating silent compliance gaps.
Conclusion
Ensuring your website’s cookie banner is fully compliant with GDPR and other global privacy laws is essential not only for avoiding hefty fines but also for building user trust. By implementing clear, transparent, user-friendly consent mechanisms that respect explicit consent and offer equal options to accept or reject cookies, you can meet legal requirements and strengthen your brand reputation. Using a robust consent management platform like Pandectes helps automate compliance, manage consent records, and adapt to evolving guidelines from data protection authorities, making it easier for Shopify stores to navigate the complex global landscape of privacy regulations.